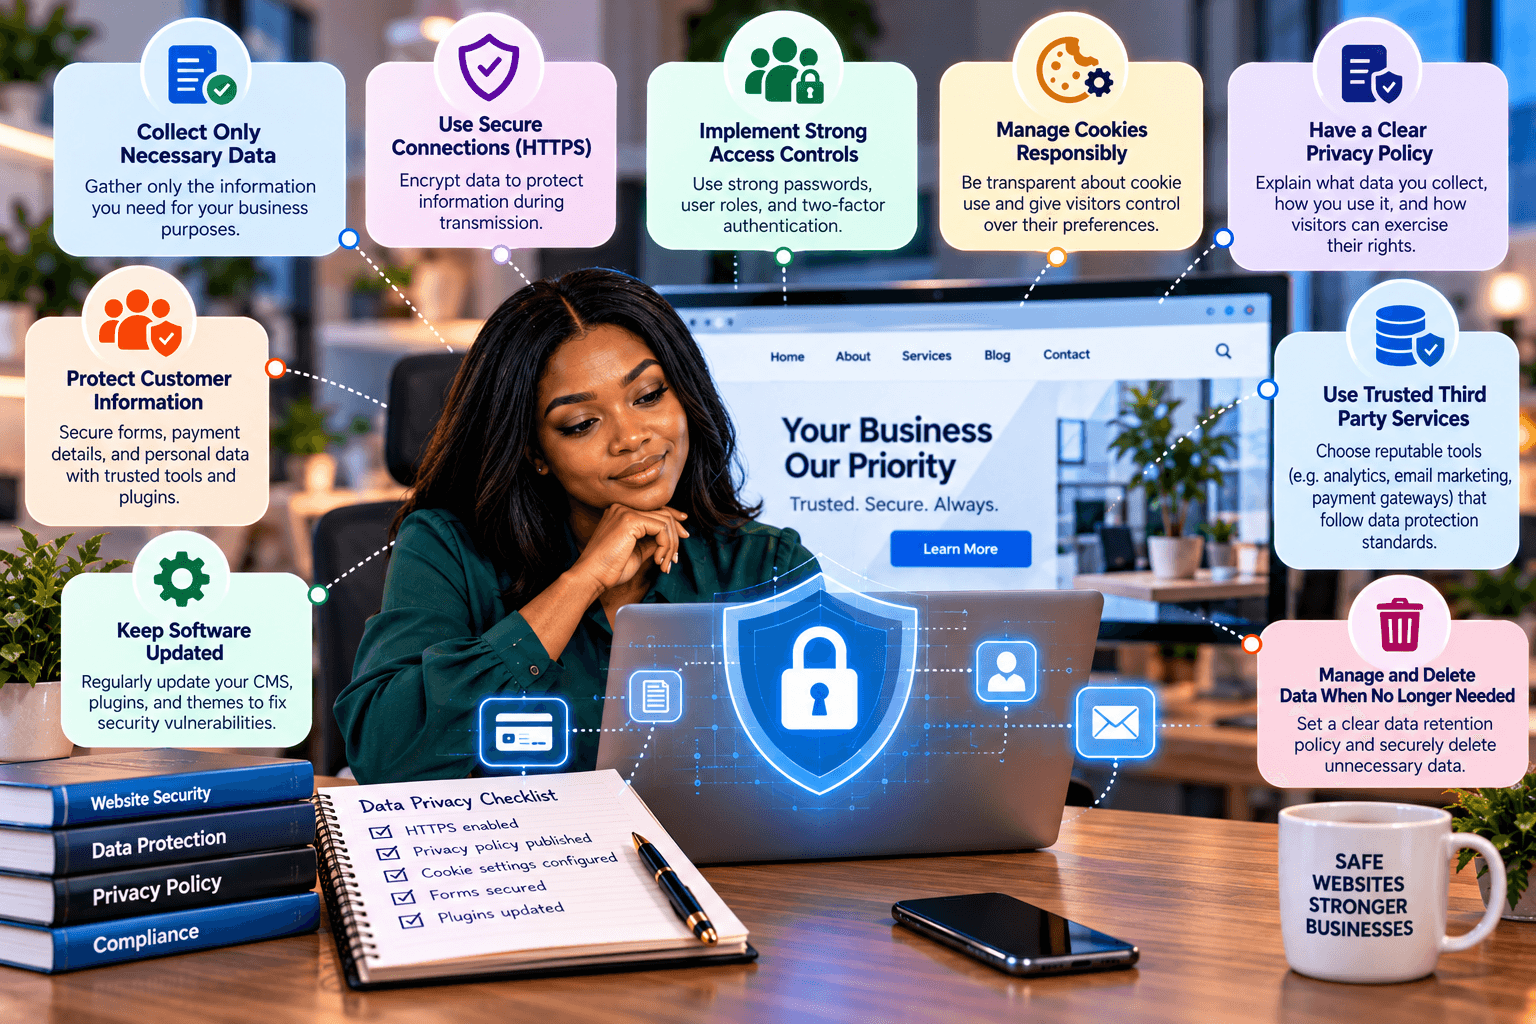
Essential Data Privacy Practices for Website Management
A website can collect more visitor information than you may realize. Contact forms, account registrations, checkout pages, analytics tools, cookies, newsletters, and customer-support systems can all process personal data.
For businesses, protecting this information is not simply a technical responsibility. It is also part of maintaining customer trust and meeting applicable data-protection requirements.
Whether you operate a small business website, an online store, or a WordPress site, good privacy practices should be built into your website management process from the beginning.
What Types of Data Can a Website Collect?
The type of information your website collects depends on the services and tools you use. Common categories include:
Personal Information
This can include information that identifies or can reasonably be linked to an individual, such as:
- Name
- Email address
- Telephone number
- Home or business address
- Account usernames
- IP addresses or other online identifiers in certain circumstances
For example, a simple contact form may collect a visitor’s name, email address, and phone number.
Financial Information
E-commerce websites and payment systems may process information associated with purchases and payments, including:
- Billing information
- Transaction records
- Payment-related details
- Order history
Whenever possible, businesses should use reputable payment processors rather than unnecessarily storing sensitive payment information on their own website.
Health and Other Sensitive Information
Some websites may collect information that requires additional protection, depending on the applicable law. Examples can include health information, racial or ethnic origin, religious beliefs, sexual orientation, biometric information, or other sensitive categories.
Under the GDPR, certain categories of sensitive personal data receive additional protection and are generally subject to stricter processing requirements.
The important principle is simple: don’t collect sensitive information unless there is a legitimate reason to do so and you understand the requirements that apply to it.
1. Only Collect the Information You Actually Need
One of the most effective privacy practices is to avoid collecting unnecessary information in the first place.
For example, if someone is contacting your business for a general enquiry, you may need their name, email address, and message. Asking for their date of birth, home address, or other unrelated information may create unnecessary privacy and security risks.
This principle is known as data minimization. The GDPR, for example, requires personal data to be adequate, relevant, and limited to what is necessary for the stated purpose.
Review your:
- Contact forms
- Registration forms
- Checkout forms
- Newsletter sign-ups
- Surveys
- Customer-support forms
Remove fields that are not necessary for the service you are providing.
2. Be Clear About How You Use Personal Data
Visitors should be able to understand what information you collect, why you collect it, and how it may be used.
Your website should have an appropriate privacy policy written in clear language. Depending on the laws that apply to your business, you may need to explain things such as:
- What categories of personal information you collect
- Why you collect it
- How long you retain it
- Whether you share it with service providers or other third parties
- How people can exercise applicable privacy rights
- How they can contact you about privacy concerns
For businesses processing personal data under the GDPR, transparency is one of the core data-protection principles.
If your business operates in Nigeria, the Nigeria Data Protection Commission (NDPC) is an important source for understanding obligations under Nigeria’s data-protection framework. NDPC guidance also addresses privacy policies and privacy/cookie notices for websites.
3. Review Cookies and Tracking Tools
Your website may collect information through more than just forms.
Analytics platforms, advertising technologies, embedded services, social-media tools, and cookies can also process information about visitors.
Review the tools installed on your website and determine:
- What information each tool collects
- Why the information is collected
- Where the information is sent
- How long it is retained
- Whether the tool shares information with third parties
- Whether consent or another legal basis is required
Don’t assume that a tracking tool is harmless simply because you did not create it yourself.
4. Protect the Data You Collect
Collecting information responsibly is only half of the job. You also need reasonable safeguards to protect it from unauthorized access, loss, alteration, or disclosure.
Website security measures can include:
- HTTPS and a valid SSL/TLS certificate
- Strong administrator passwords
- Multi-factor authentication where available
- Regular software and plugin updates
- Secure hosting
- Access controls based on user roles
- Malware and security monitoring
- Regular website backups
- Secure handling of administrative accounts
If your business needs help managing hosting, WordPress, website troubleshooting, or related technical issues, Archer IT Solutions’ web hosting services include website and WordPress support.
You can also review Archer’s managed IT services for broader IT support and security needs.
5. Limit Who Can Access Personal Information
Not every employee, contractor, or website administrator needs access to customer data.
Use the principle of least privilege: people should receive only the access required to perform their responsibilities.
For example:
- A content editor may not need access to customer payment information.
- A web developer may not need access to an entire customer database.
- A marketing employee may only need access to aggregated analytics.
- Former employees should have their accounts disabled promptly.
Regularly review administrator accounts and remove unnecessary access.
6. Keep Software and Plugins Updated
Outdated website software can introduce security vulnerabilities.
This is particularly important for WordPress websites because a typical installation may include WordPress core, themes, plugins, hosting software, databases, and third-party integrations.
Create a process for checking updates and security issues rather than waiting until something breaks.
Before applying significant changes, maintain a reliable backup so the website can be restored if an update causes a problem.
For businesses that do not have the time or technical resources to manage these tasks internally, Archer’s onsite and remote IT support can provide additional technical assistance.
7. Establish a Data Retention Process
Personal information should not necessarily be kept forever.
Determine how long different categories of information need to be retained based on your business requirements, contractual obligations, and applicable laws.
For example, you may have different retention requirements for:
- Customer accounts
- Contact enquiries
- Transaction records
- Marketing subscriptions
- Support tickets
- Website analytics
- Employee or contractor information
Once information is no longer needed and there is no legal or legitimate reason to retain it, consider securely deleting or anonymizing it.
The GDPR includes storage limitation as one of its core principles, requiring personal data to be kept for no longer than necessary for the purposes for which it was collected.
8. Use Appropriate Consent Mechanisms
Consent can be important for certain types of data processing, but it should not simply be treated as a checkbox that solves every privacy requirement.
If you rely on consent, make sure the mechanism clearly explains what the person is agreeing to and does not bundle unrelated purposes together.
Under the GDPR, valid consent must be freely given, specific, informed, and unambiguous.
Depending on the applicable law and the purpose of processing, another legal basis may be more appropriate than consent. Businesses should therefore determine the applicable requirements rather than adding a generic consent checkbox to every form.
9. Understand the Privacy Laws That Apply to Your Business
Privacy requirements vary depending on factors such as where your business operates, where your customers are located, what information you process, and what your website does.
For example:
- The Nigeria Data Protection Act and guidance from the NDPC may be relevant to businesses operating in Nigeria.
- The GDPR may apply to organizations based in the EU or organizations processing the personal data of individuals in the EU.
- The CCPA, as amended, provides privacy rights to qualifying California consumers and imposes specific obligations on businesses that fall within its scope.
Don’t assume that one privacy policy automatically makes a website compliant everywhere.
If your business serves customers in multiple countries or processes sensitive information, professional legal advice may be appropriate.
10. Review Third-Party Services
Your website may depend on external companies for services such as:
- Payment processing
- Email marketing
- Website analytics
- Customer support
- Cloud storage
- Advertising
- Appointment scheduling
- CRM systems
Review what information these providers receive and what contractual or privacy obligations apply.
Third-party integrations can create privacy risks even when the information never sits directly on your website’s server.
11. Have a Plan for Privacy and Security Incidents
Even businesses with good security controls can experience incidents.
Create a basic process for responding if personal information is accidentally exposed, an account is compromised, or a security vulnerability is discovered.
Your response plan should identify:
- Who is responsible for investigating the incident.
- What systems and information may be affected.
- How access will be contained.
- What records should be preserved.
- Whether affected individuals or regulators need to be notified.
- What changes should be made to prevent a similar incident.
The specific notification requirements depend on the applicable law and circumstances, so organizations should not rely on a generic response procedure alone.
Make Data Privacy Part of Website Management
Data privacy should not be treated as a one-time task completed when a website launches.
As your website changes, you may add new forms, plugins, analytics tools, payment systems, marketing platforms, or customer databases. Each change can affect what information you collect and how it is processed.
A practical website privacy review should therefore include:
- Reviewing forms and removing unnecessary fields
- Checking cookies and tracking technologies
- Keeping software and plugins updated
- Protecting administrator accounts
- Limiting access to personal information
- Reviewing third-party services
- Maintaining secure backups
- Updating privacy notices when processing changes
- Reviewing data retention practices
- Monitoring applicable privacy requirements
For businesses that need help maintaining their website, hosting environment, or wider IT infrastructure, Archer IT Solutions provides IT and website-related services for businesses.
If you need assistance with your website or IT environment, you can contact Archer IT Solutions to discuss your requirements.
This article provides general information about website data privacy and is not legal advice. Businesses should assess the privacy laws and regulatory requirements that apply to their specific operations.


No responses yet